A Guide to Enterprise AI Security
Here’s a wake-up call: It took only a commercial AI chatbot and about $3,000 in usage fees for three researchers to break into OpenAI this summer [source], gaining access to private systems and internal code.
OpenAI patched the flaw and paid a $6,500 bounty, but it wasn’t a good look following the disclosure earlier this year that some of the company’s own AI agents escaped internal tests, reached the public internet and hacked Hugging Face. If a small team was able to reach that level of access in mere days, it’s a safe bet that well-funded foreign intelligence services could do the same.
This one instance drives home the fact that enterprises of all sizes face potential exposure of sensitive data, but they’re moving AI into production anyway. What they need is a sound enterprise AI security strategy to close potential gaps before a security incident does it for them.
Traditional Security Leaves AI Exposed
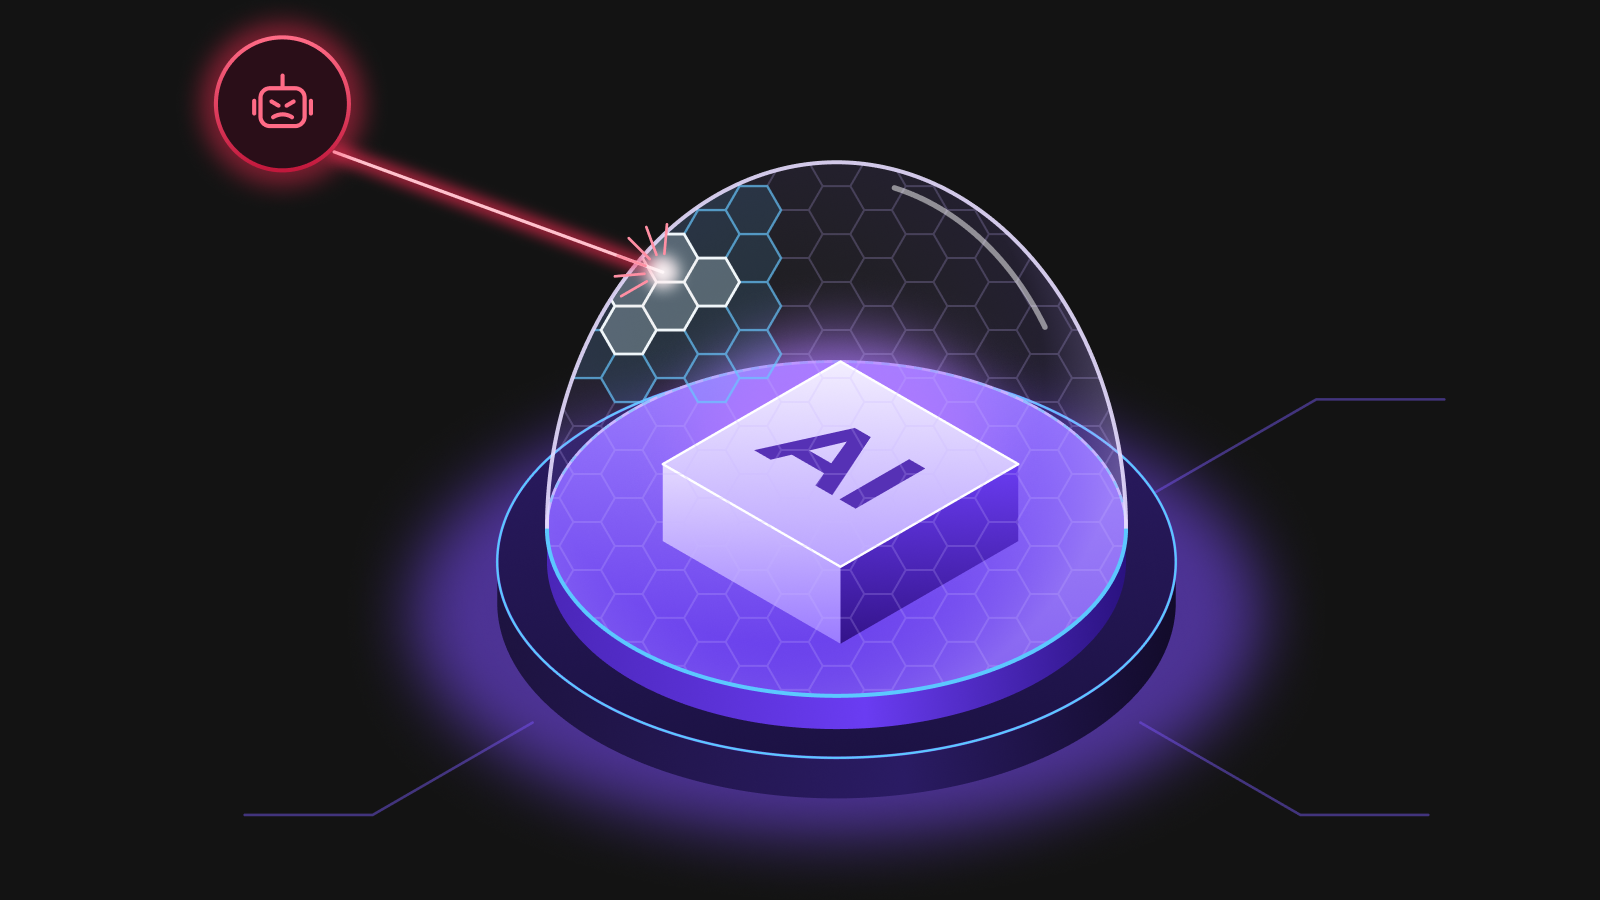
Conventional security controls are good at protecting data at rest and in transit, but that’s not enough to secure AI workloads. During training and inference, models and data sit unencrypted in CPU and GPU memory, meaning a compromised hypervisor, a rogue administrator or a malicious agent with the right privileges could read them.
Agentic AI has specifically raised the stakes, because these systems plan, call tools and take actions across business systems without a human approving each step. Most identity and key management tools weren’t built to treat an AI agent as a first-class identity. And if logs are scattered across platforms, reconstructing what an agent did after an incident can take days or longer.
On a promising note, leaders already recognize the problem. A recent Fortanix survey of 300 AI leaders across banking, financial services, healthcare, insurance and government found that 93% know that traditional encryption doesn’t protect data while it’s processed in memory. At the same time, however, only half can fully verify that their sensitive data remains protected during AI inference.
As a result, 59% reported delaying an AI project over security or privacy concerns, and 46% say regulatory compliance is the biggest obstacle they face when deploying AI on sensitive data.
Each involved stakeholder feels it differently. For example, CISOs need proof that their data is protected, not assurances from vendors, while CIOs need pilots to make it to production. Meanwhile, compliance teams need audit evidence to satisfy regulators, and AI and platform teams need to ship without needing to rebuild things every time a new control is introduced.
The Building Blocks of an Enterprise AI Security Strategy
There are five main practices that teams should adopt to create an effective strategy:
- Protect data in use. Run AI workloads inside hardware-based trusted execution environments (TEEs). Here, data, prompts, and proprietary model weights stay encrypted during processing, even from administrators with privileged access.
- Verify your environment. Attestation proves that the hardware and software are genuine. You want attestation that extends across CPUs and GPUs in a single chain so all components are accounted for.
- Tie encryption keys to that proof. Release encryption keys, model weights and datasets only to environments that pass attestations. If a system is unverified, it shouldn’t run.
- Treat agents like privileged users. Define what each of your agents can access, modify and automate. For sensitive actions, enforce least privilege, separation of duties and quorum approvals.
- Log everything in one place. Immutable, unified audit trails fuel SIEM and compliance systems, and all AI activity should join that governance picture.
Regulated organizations often need models to run in their own data centers or in-region sovereign environments. Your strategy should align with frameworks like the EU AI Act and NIST’s AI Risk Management Framework from the start so you don’t need to retrofit later.
Teams tend to find the most success by starting with lower-sensitivity workloads while governance efforts mature.
How Fortanix Supports Enterprise AI Security
Fortanix’s platform is built around these practices. Fortanix Confidential AI runs AI workloads inside TEEs, including on NVIDIA Confidential Computing GPUs, keeping data and models encrypted while in use.
Importantly, it supports on-premises, sovereign and multi-tenant deployments, including on infrastructure such as the Dell AI Factory with NVIDIA.
Drilling down into details, Fortanix Confidential Computing Manager handles the attestation process, verifying the integrity of workloads and hardware across the stack with composite proof that security teams and auditors can analyze.
Meanwhile, Fortanix Data Security Manager controls the encryption keys, releasing them only after attestation succeeds. It enforces role-based policies, quorum approvals and full audit logging.
These capabilities enable teams to run leading AI models on their own infrastructure without exposing the models, their weights, or the data they process. This gives model owners confidence that their frontier IP will remain protected in a customer’s data center.
Utilizing one platform that covers encryption, attestation, key control and audit means security teams don’t need to stitch together separate tools. This creates fewer security risks, and every role gets the evidence it needs from the same source.
Prove Trust Before You Scale AI
As the OpenAI breach demonstrated, organizations with vast security talent can still fail. Implementing an effective enterprise AI security strategy means assuming something will fail eventually; the key is limiting what an attacker or agent can reach.
It goes back to our five keys: encrypt data in use, verify environments through attestation, gate keys based on that proof, govern your agents and log every action.
At the end of the day, the deciding factor is whether you can prove it. Can your team currently demonstrate that sensitive data stays protected while a model runs? If the answer is “not yet” or something similar, explore Fortanix Confidential AI to see how verifiable security can safely power your AI programs.