Fortanix | Cisco Solution Built


Enable Secure Enterprise AI Without Slowing Innovation
Enterprises are rapidly adopting AI to drive productivity and competitive advantage, but most struggle to move beyond pilots. Scaling AI infrastructure on premises, in AI factories, or clouds, from centralized model training to low-latency inferencing across distributed environments, demands seamless integration of compute, networking, storage, observability, and AI software, while simultaneously meeting stringent security requirements for the full stack, complex compliance mandates, and expanding security vulnerabilities. Traditional security protects data at rest and in transit, but does not protect model weights, the critical AI AP, and inference data in memory during production, exactly where AI workloads are most vulnerable.
Cisco Secure AI Factory with NVIDIA and Fortanix Confidential AI Solution
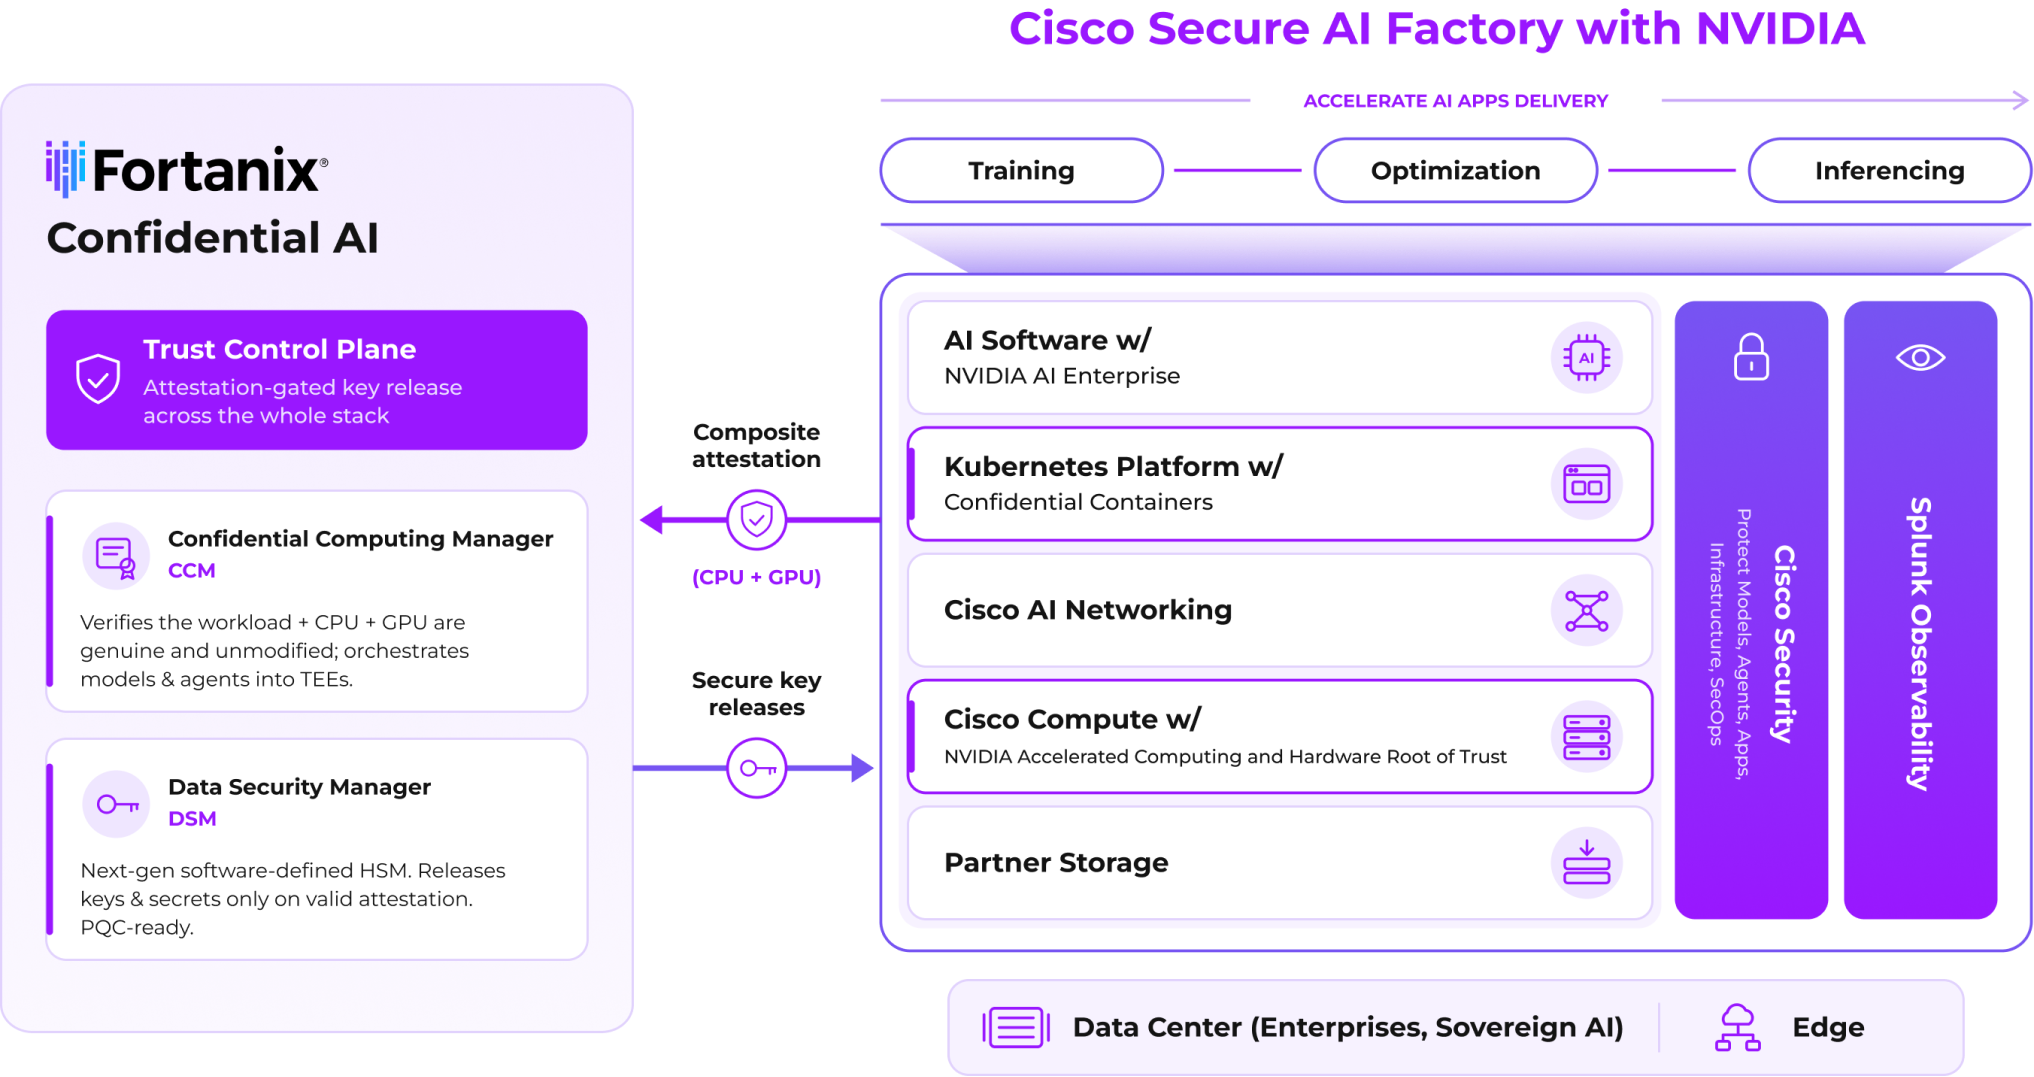
Jointly, Fortanix, Cisco, and NVIDIA deliver a pre-validated, secure and scalable AI infrastructure, engineered with end-to-end security across the full AI lifecycle, with high-performance scalability and deployment simplicity. AI workloads run inside Trusted Execution Environments (TEEs) on Cisco servers with NVIDIA GPUs supporting Confidential Computing, while the Fortanix Confidential AI solution provides the control plane for composite attestation, secure key release, and policy enforcement. With Fortanix and Cisco, enterprises can now unlock the full value of their AI investments. From running frontier models on sensitive data in their own environments, to achieving AI workload isolation in multitenant AI factory deployments, or meeting the strictest sovereign AI requirements.
Use Cases

Secure Distribution of Proprietary Models
Model weights are encrypted at source and decrypted only inside an attested TEEs, giving model owners cryptographic guarantees over their IP, while enterprises run best-in-class models on their own data without exposing prompts or outputs to the model vendor.

Multi-Tenancy and Segmentation for AI Factories
Each tenant runs in its own Confidential VM on shared Cisco accelerated compute infrastructure with hardware-enforced isolation and tenant-own key release. Shared economics with isolated trust, a single infrastructure every tenant can rely on.

Sovereign AI Clouds
Governments, financial services, healthcare, and defense enterprise can now run AI on previously inaccessible sensitive data in fully attested AI environments within a target jurisdiction, with cryptographic, auditor-grade proof.
Pre-Validated, Secure, and Scalable AI Infrastructure
Cisco extends protection across the AI environment with Hybrid Mesh Firewall, a distributed security fabric that orchestrates consistent policy across enforcement points from the network edge to the workload. Cisco Secure Firewall provides threat inspection and policy enforcement at critical network control points, while Cisco Identity Services Engine (ISE) supplies identity and device context the who and what requesting access to enable granular, least-privilege segmentation around the confidential computing environment. Together with Cisco secure networking, these controls restrict unauthorized access and lateral movement before traffic reaches protected AI models and data.
Fortanix Confidential AI ensures the runtime protection of the AI workload, protecting the assets while they are in use. Fortanix Confidential AI cryptographically verifies every remote TEE to confirm that hardware isolation and the exact code are genuine and untampered with, thus ensuring AI workload protection based on cryptographic proof, not trust.
1. Secure Enclave Management
Fortanix Confidential Computing Manager (CCM) creates, manages, and enforces policy controls to run the AI workloads in hardware-isolated enclaves, isolated from the OS, hypervisor, and administrators. CCM currently supports composite attestation for:
- Intel TDX and AMD SEV-SNP CPU
- NVIDIA Blackwell and Hopper Confidential Computing GPUs
2. Secure Key Release
Encryption keys are released only to verified, attested enclaves. Fortanix Data Security Manager (DSM), a FIPS 140-2 Level 3 HSM with built-in Key Management, enforces strict key custody so sensitive data and models stay encrypted in memory, inaccessible to anyone outside the TEE.


