What is a Cryptographic Inventory?
Nobody knows when quantum computing will become a mainstream reality, but organizations are increasingly betting on sooner rather than later.
Microsoft is just one example, saying it will transition critical products and services to post-quantum cryptography (PQC) by 2029 [source]. The company said cryptographically relevant quantum computers could arrive sooner than expected, and that organizations should start preparing now.
Google, Cloudflare, and many others have made similar commitments as the mystery deadline nears. The reality is that these hyperscalers have large engineering teams and a head start, luxuries that most enterprises don’t have.
But even before replacing a vulnerable algorithm to become PQC-ready, organizations first need to determine where their cryptography lives and what it protects.
Cryptography Grew Faster Than It Was Tracked
Going back years or even decades, encryption spread across organizations on a project-by-project basis. Development teams would generate keys for new apps, and key management services from AWS, Azure, and Google Cloud popped up as organizations moved to the cloud.
The sprawl accumulated quickly.
Today, it’s common for an enterprise to run several key management systems across clouds, use legacy hardware security modules (HSMs) in data centers, with an unknown number of keys/certificates hard-coded in source code, file systems, and libraries. Needless to say, this is a problem even before quantum computing arrives.
PQC is already making an impact, with digital thugs using “harvest now, decrypt later” techniques: stealing encrypted data today and unlocking it once quantum computers mature.
If an organization has data that must stay confidential beyond that point, the hard reality is that it’s likely already exposed. But you can’t start a migration before you know what you have.
This Is What Cryptographic Inventory Means
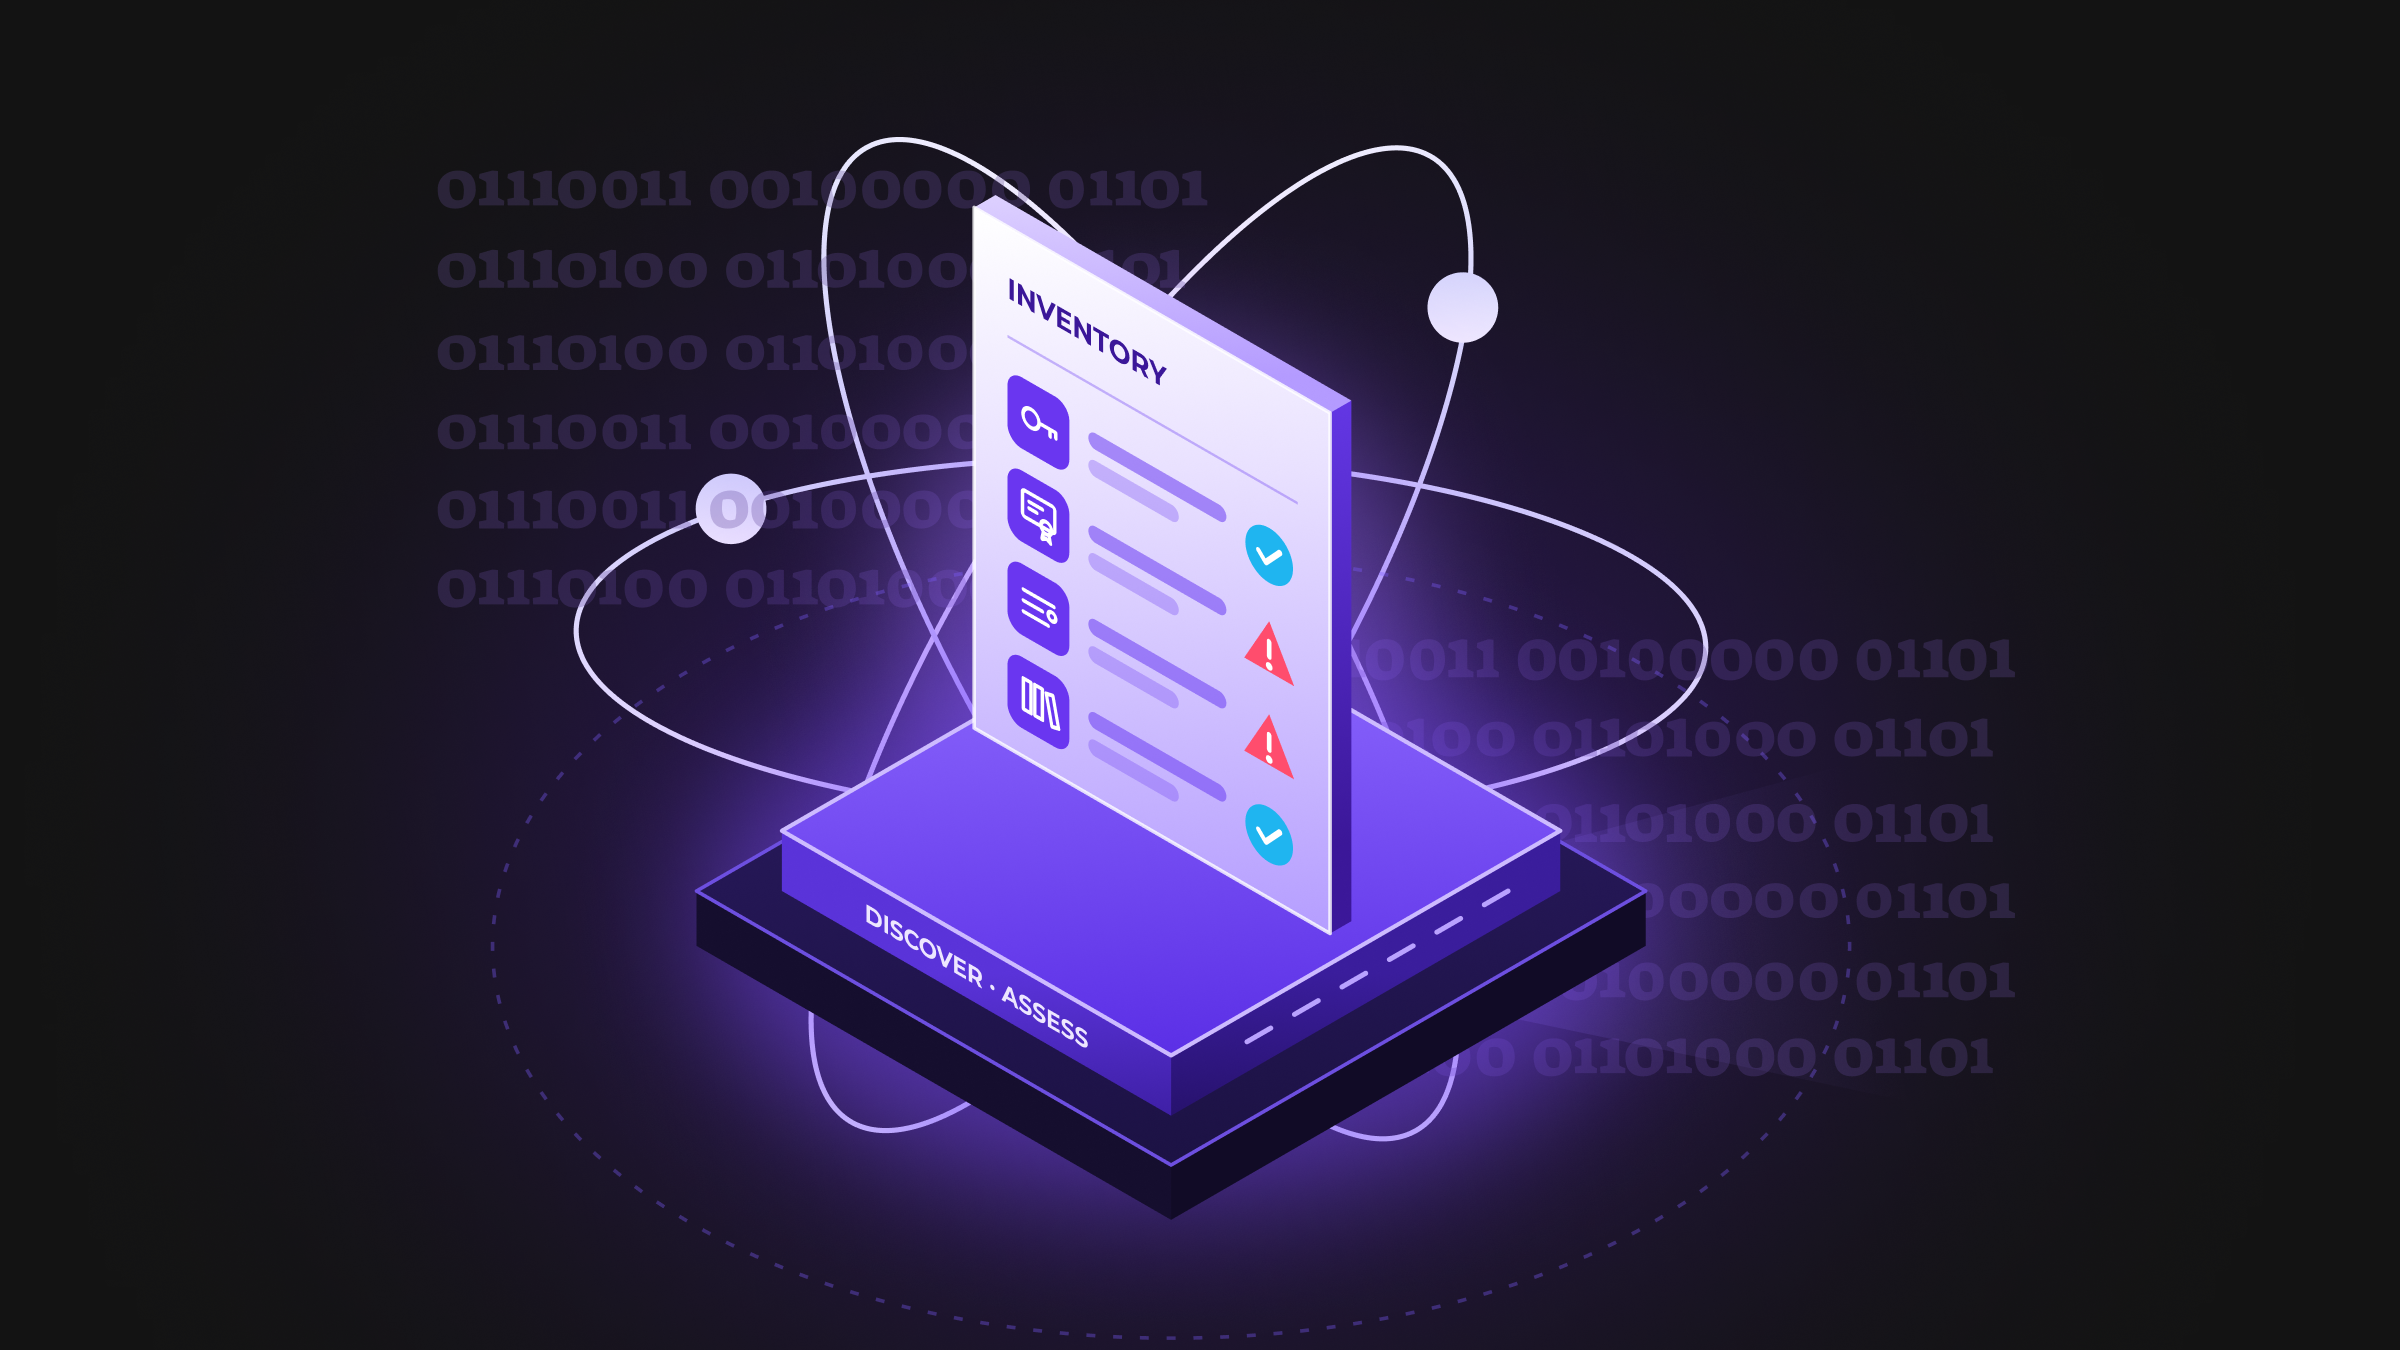
A cryptographic inventory is a continuously updated record of every cryptographic asset in your environment, plus the context needed to act on it. This includes encryption keys, digital certificates, algorithms, cryptographic libraries and protocols, and all the applications, services, and data each one protects.
Understanding the relationships behind each key is vital. Knowing an RSA key exists isn’t enough; you need to know what it encrypts, whether it’s been rotated recently, and whether it’s in a cloud KMS outside your governance policies.
As part of Microsoft’s commitment, the company said it will remove hard-coded algorithmic assumptions and build systems in which algorithm upgrades are routine rather than emergencies. That’s the level of crypto-agility that every organization should strive for, but it first requires knowing where every algorithm runs.
*Learn more about why quantum readiness is urgent
What to Look for in a Cryptographic Inventory Solution
Not all discovery tools produce a useful inventory list. Security teams evaluating options should look for:
- Wide discovery coverage. You don’t want any blind spots across KMS services, on-premises HSMs, databases, code repositories, file systems, containers and certificate management platforms.
- Mapping keys to services. You need to know which keys protect which services and resources, so you can understand the impact of any change.
- Quantum risk classification. Your tool should flag which assets are vulnerable to quantum attacks and which already align with NIST’s post-quantum standards.
- Continuous scanning. A point-in-time snapshot is useless when things change so rapidly, particularly in the age of agentic AI.
- A clear path to remediation. You need to know ahead of time what to do when something goes wrong, because something will go wrong.
Fortanix Builds and Manages Cryptographic Inventory
Fortanix approaches cryptographic inventory with a discover-assess-remediate mentality.
Fortanix Key Insight handles discovery and assessment, scanning across cloud services, on-premises databases, Git repositories, and container environments. It connects to external key sources and certificate management platforms to pull in certificates that many conventional scans miss.
Key Insight then maps each key to the services it protects and flags the weak algorithms, missing rotation policies and unencrypted data it finds. A PQC Central dashboard labels every asset as PQC-ready or PQC-vulnerable across your cloud, on-premises and HSM environments. Teams can see what needs to be fixed first, and auditors or partners can easily access the data they need.
Fortanix Data Security Manager (DSM) handles the management and remediation part of the equation. DSM combines centralized key management with a FIPS 140-2 Level 3-certified HSM, keeping an accurate, audit-ready record of managed keys. It also integrates with external key services and bring-your-own-key models so you can manage them all under one set of policies.
In tandem, Fortanix KI will provide the single source of truth for Inventory, while DSM helps navigate to the next step of assessing which Algorithm is best suited for the application from pqc standpoint.
Rule of Thumb: Start with What You Can See
Tech leaders and governments around the world have set tangible post-quantum goals, and enterprises are following suit. The most successful will be those who first find every key, certificate, and algorithm in their environment.
Only with a full cryptographic inventory can you devise a post-quantum migration plan. But tidying up your inventory has immediate benefits as well, such as fewer certificate outages, faster audits and more control over key sprawl.
We don’t know the exact date a quantum computer will break RSA. But what we can know is where your RSA keys are when the day comes.
If you want to see what’s in your environment, request a demo of Fortanix Key Insight and Fortanix DSM and start building your comprehensive cryptographic inventory.