Full Protection for Enterprise Data, AI Models, and Agents
Fortanix Confidential AI secures sensitive data, proprietary frontier models, and agents across the full AI lifecycle. The joint Fortanix-NVIDIA solution, built on Confidential Computing, keeps both data and model IP inaccessible to the underlying infrastructure, with verifiable trust and cryptographic guarantees. Whether you run AI workloads in confidential VMs or Confidential Containers (CoCo) on Kubernetes, Fortanix attests every workload and releases keys only to verified environments. From scaling enterprise AI and deploying frontier AI on premises to securing multi-tenant AI Factories and building sovereign AI clouds, Fortanix Confidential AI is your proven path to AI innovation, with security, trust, and sovereignty at the core.
Confidential AI Ecosystem


More Ways Fortanix
Confidential AI Helps
Fortanix Confidential Al help eliminate the barrier of Al adoption by protecting both proprietary Al models and sensitive data while in use to accelerate Al innovation without compromising security, trust, and sovereignty.

AI Labs
Deploy frontier models wherever enterprise data lives, with your IP fully protected.

Multitenant AI Factories
Turn multi-tenancy into a trusted, verifiable architecture.

Sovereign AI Cloud
Guarantee data residency and in-border AI innovation
Secure Environment for AI Workloads
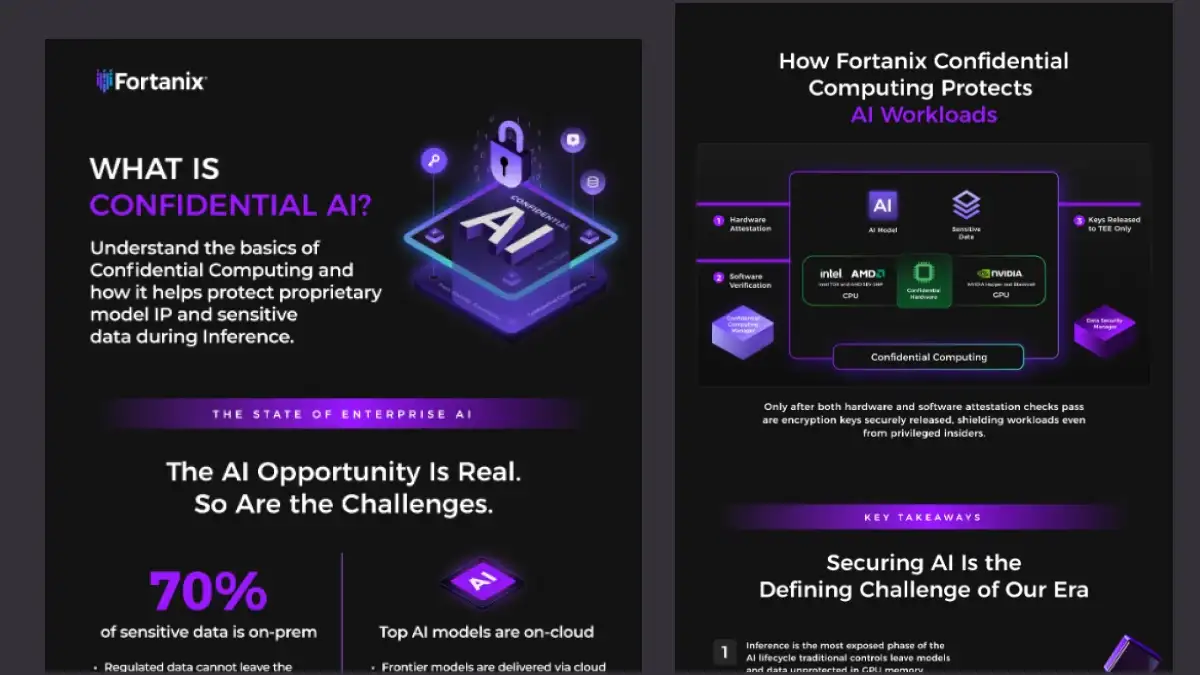
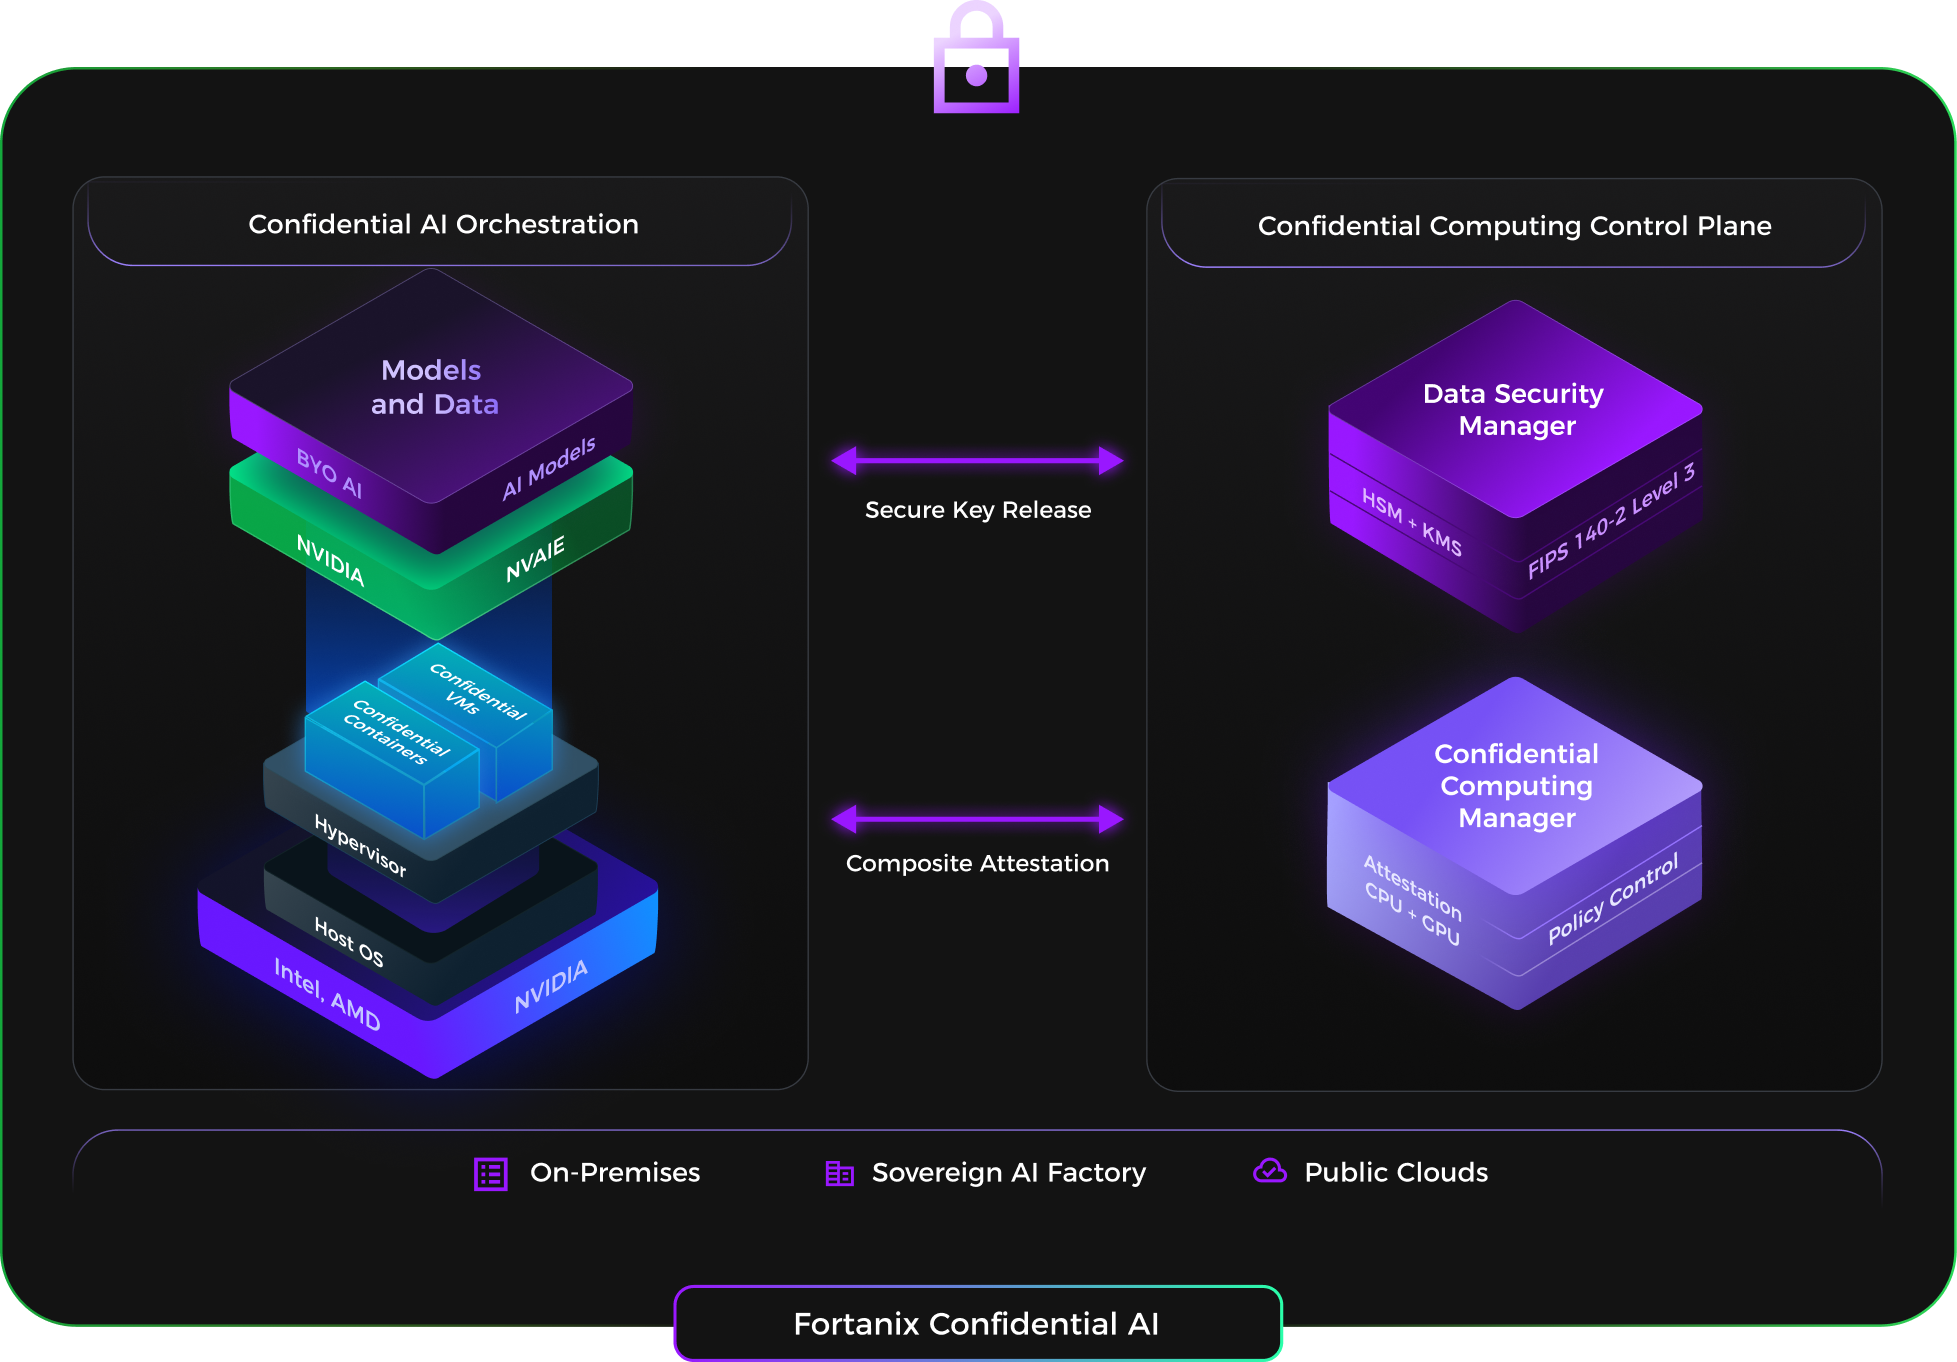
Whether your AI runs on premises or in public clouds, Confidential CPUs and GPUs ensure in-memory encryption, keeping sensitive data, model weights, and inference protected, even from privileged insiders. Use the Trusted Execution Environments (TEEs) to
- Ensure data, models, and agents security
- Run best in class AI on premises
- Meet regulatory requirements
*Supported public clouds: Azure and Google

Verifiable Infrastructure Integrity
Composite attestation for CPU and GPU create a single chain of trust. Verify exactly what AI workload is running with hardware-signed proof. The confidential control plane allows you to
- Create Confidential VMs and Confidential Containers
- Set policy controls

Secure Key Release
Access to datasets and model artifacts is allowed only after verified attestation. Decryption happens only within verified, isolated environments. Drive crypto agility with
- FIPS 140-2 Level 3 Certified HSM with built-in KMS
- Latest NIST-approved PQC algorithms





Benefits

Protect models, agents, and data while in use to securely scale AI

Attest every workload, hardware and software for trusted and verifiable proof of security

Ensure data stays compliant, governed, and sovereign, no matter where the workloads run
Resources
Here are some of latest news, blogs, resources, events, and more