Confidential AI Now Runs on Kubernetes with CNCF Confidential Containers
Putting AI in containers doesn’t change the threat: models, agents, and data are still exposed while they run. Fortanix Confidential AI now supports CNCF Confidential Containers (CoCo), running AI workloads on Kubernetes inside hardware-based TEEs on confidential CPUs and GPUs, with every workload verified before a single key is released. Available now, with support from 22 industry leaders including Alpha Compute, AMD, Cisco, CrowdStrike, Deepgram, Dell, ElevenLabs, Fujitsu, Gnani, H2O.ai, HPE, Intel, Klique, Personal AI, Rafay, Red Hat, Resemble AI, Spectro Cloud, Supermicro, Technology Innovation Institute (TII), TELUS and VAST Data.
The AI Trust Gap: State of Enterprise AI Deployment Report
93% of AI leaders know traditional encryption doesn’t protect data while AI processes it. Only half can fully verify that protection is in place during inference. Fortanix and Atomik Research surveyed 300 AI leaders across banking, financial services, healthcare, insurance, and government to find out what is holding back deployment on sensitive data.
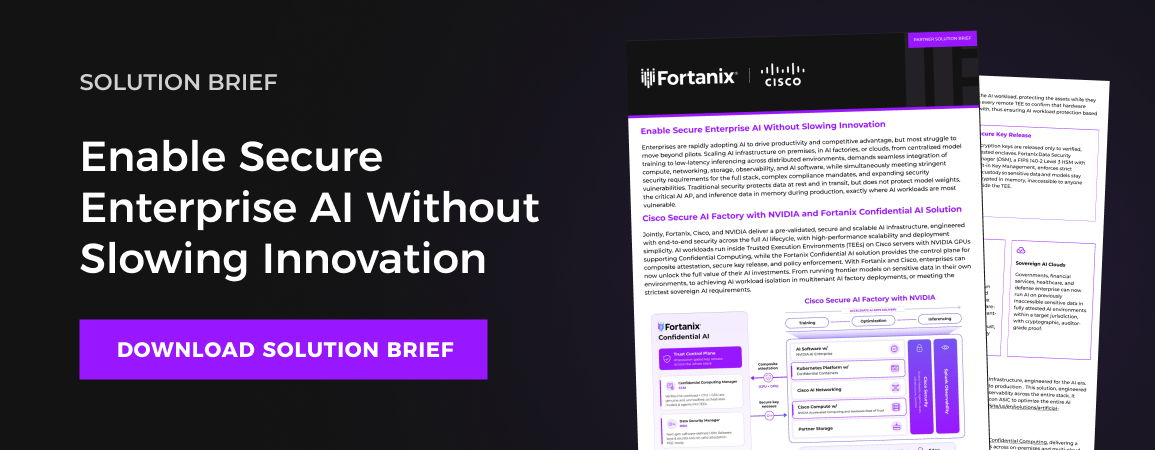
Enable Secure Enterprise AI Without Slowing Innovation
Most enterprises struggle to move AI past pilots, and traditional security leaves model weights and inference data exposed in memory while they run. Fortanix, Cisco, and NVIDIA bring Confidential AI to Cisco Secure AI Factory: workloads run in TEEs on Cisco servers with NVIDIA Confidential Computing GPUs, while Fortanix handles attestation and secure key release. Cisco’s new design guide shows it end to end: an encrypted, GPU-enabled container running on Kubernetes on a Cisco UCS C240 M8, with key release gated by Fortanix attestation.
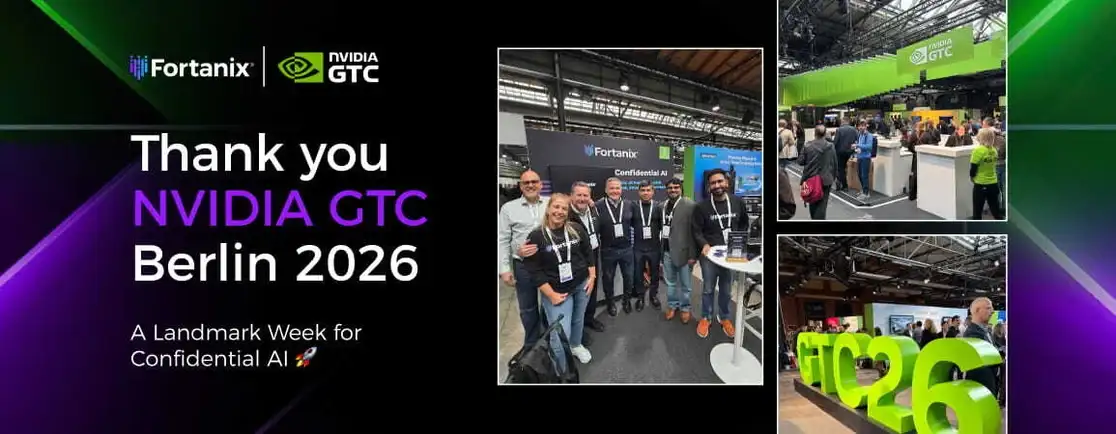
Fortanix at NVIDIA GTC Berlin 2026: Recap
Three days at STATION-Berlin, and the conversation at Booth 7017 kept coming back to AI model security. Visitors saw Fortanix Confidential AI protect sensitive data and model weights while running on NVIDIA GPUs, with cryptographic attestation verifying the environment before any key is released. Many were glad to learn that models can be deployed locally with stronger protection. Thank you to everyone who stopped by.
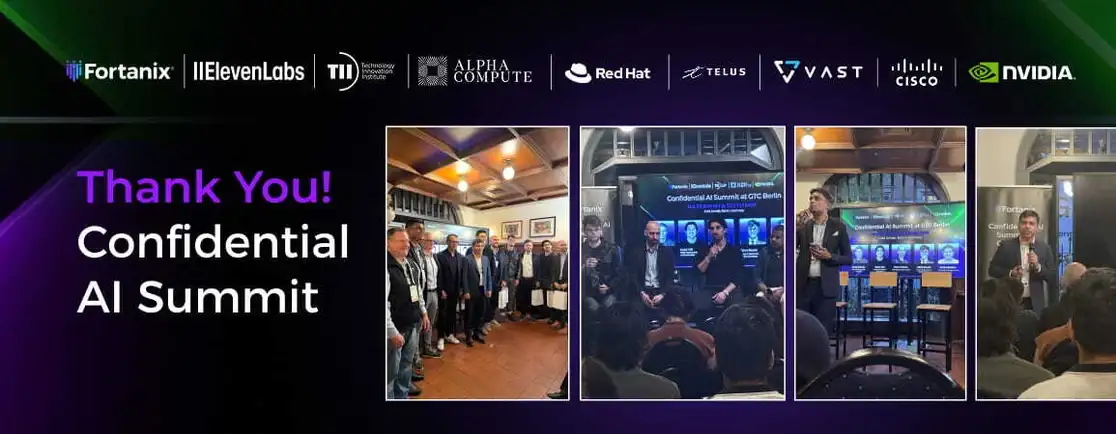
Confidential AI Summit Berlin: Recap
Fortanix hosted an invitation-only Confidential AI Summit in Berlin on October 22, together with NVIDIA ecosystem partners, an evening on building AI that is trusted, secure, and sovereign. Fortanix CEO Anand Kashyap opened, and CPO Anuj Jaiswal moderated two panels: “The Chain of Trust for Confidential AI” and “The Confidential and Sovereign AI Factory.”
Thank you to our panelists from NVIDIA, ElevenLabs, the Technology Innovation Institute, Alpha Compute, Red Hat, TELUS, VAST Data, and Cisco for sharing their perspectives. And thank you to everyone who joined us in Berlin.
300 AI Leaders Told Us What Happens When Security Falls Short
Do You Know Enterprises Prefer Running AI Models On-Premise Securely?
How Fortanix Confidential AI Works as a Trusted Layer
Protecting AI Workloads on Kubernetes with Fortanix and Confidential Containers
Why Confidential AI Matters for Secure AI Deployment
Quantum Key Distribution: What Is It and How Does It Work?
Confidential AI at Container Speed
Intel Retires SGX: What It Means for Fortanix
A Guide to Enterprise AI Security
The Enterprise AI Trust Gap in Regulated Industries
Enterprise AI Security: How to Protect Data, Models, and AI Agents
Fortanix EDP Coming to More Platforms, Keeping TCB Small
How to Prepare for Post-Quantum Cryptography
A Guide to Post-Quantum Cryptography (PQC) Readiness
A Technical Guide for Model Builders on Protecting AI Model IP
What is a Cryptographic Inventory?
PQC Algorithms Explained: ML-KEM, ML-DSA, and SLH-DSA